AI regulation in Switzerland: what already applies
Waiting for a Swiss AI law is not worth it. Almost every AI project is already measured against law that has been in force for years.
Guide · Published 3 Aug 2026 · Updated 1 Oct 2026 · Joel Barmettler
What rules apply to AI in Swiss companies today?
There is no AI law in Switzerland. Existing law applies to AI projects: above all the revised Data Protection Act (revFADP) for personal data, plus copyright and contract law and professional secrecy. The EU AI Act, the AI law of the European Union, reaches into Switzerland only in narrowly defined cases. A Swiss draft law is due by the end of 2026.
In brief
- The revFADP has applied since 1 September 2023 and is the benchmark for almost every AI project involving personal data. Most Swiss companies barely need to consider the EU AI Act, the EU’s AI law.
- Waiting for a Swiss AI law is not worth it. On 12 February 2025, the Federal Council decided against a dedicated AI law modelled on the EU. When a bill will reach Parliament remains open.
- A company that merely uses AI in its operations is a deployer under EU law. The heavy obligations of the EU AI Act sit with the provider, meaning whoever develops an AI system and places it on the market under its own name.
- A company can slip into the provider role without meaning to. If it uses a general tool such as ChatGPT to screen job applications, it changes the tool’s intended purpose to a high-risk task and counts as the provider of a high-risk system under Art. 25 AI Act, meaning an AI application subject to the strictest obligations of the AI Act.
- Anyone bound by professional or official secrecy still needs their own risk assessment with US providers. The adequacy decision, which eases data transfers to certified US companies, has changed nothing about that.
The legal analysis in this article draws on the AI series of the Zurich law firm VISCHER, in particular the pieces by David Rosenthal on the EU AI Act and the expected Swiss regulation. We checked every date and deadline against the original sources: the text of the regulation in the EU Official Journal, the statements of the European Commission, and the communications of the Federal Council and the Federal Office of Justice. Souverana is not a law firm. This article reproduces that analysis and adds a question that a legal review does not answer: how the existing latitude can be used technically.
This article opens our series on law and regulation. It is the map; the later parts explore its individual areas in depth.
The two frameworks that matter
The same two names come up in every discussion of AI and law. They mean different things, and that difference determines what your company actually has to do.
The revFADP is Switzerland’s revised Federal Act on Data Protection, in force since 1 September 2023. It governs what a company may do with personal data, meaning information about people: customers, employees, applicants. At its core it requires five things: the processing principles, meaning purpose limitation, proportionality and recognisability, a data processing agreement with every provider that processes the data on your behalf, adequate security, transparency towards the people affected, and, for sensitive projects, an upfront risk assessment. Unlike in the EU, a private company needs no statutory basis for a processing activity. A justification only becomes necessary once the processing infringes personality rights. The law does not mention AI at all. It is built technology-neutral and applies to a language model the same way it applies to a spreadsheet. One quirk senior management should know about: fines are addressed to natural persons, up to CHF 250,000, and require intent. Only once a fine of up to CHF 50,000 is at stake can the business itself be convicted in the person’s place.
The EU AI Act is a product-safety law of the European Union. It sorts AI applications into four risk tiers:
- Prohibited are eight narrowly defined practices, such as emotion recognition in the workplace or social scoring modelled on the Chinese system. On 2 December 2026, two more are added: AI that generates intimate depictions of real people without consent, and AI that generates depictions of child sexual abuse.
- High-risk is an exhaustive list, including AI for candidate screening, credit decisions or critical infrastructure. The heavy obligations apply to these systems.
- Subject to transparency duties are applications where a person would otherwise not notice that a machine is at work, such as chatbots and AI-generated images.
- Everything else, meaning the large majority of everyday applications, is subject to no special duties.
The large general-purpose models behind services such as ChatGPT are subject to their own rules, addressed to their providers, and they do not concern you as the customer.
The AI Act is EU law. For a Swiss company, it applies only where there is a nexus to the EU market. Exactly when is covered further below.
Alongside this, further law applies that nobody calls AI regulation and that in practice often bites first: copyright law, when third-party content flows into a model; unfair competition law, in cases of deception; your own client contracts and non-disclosure agreements; and, for certain professions, professional and official secrecy.
What applies, what is coming
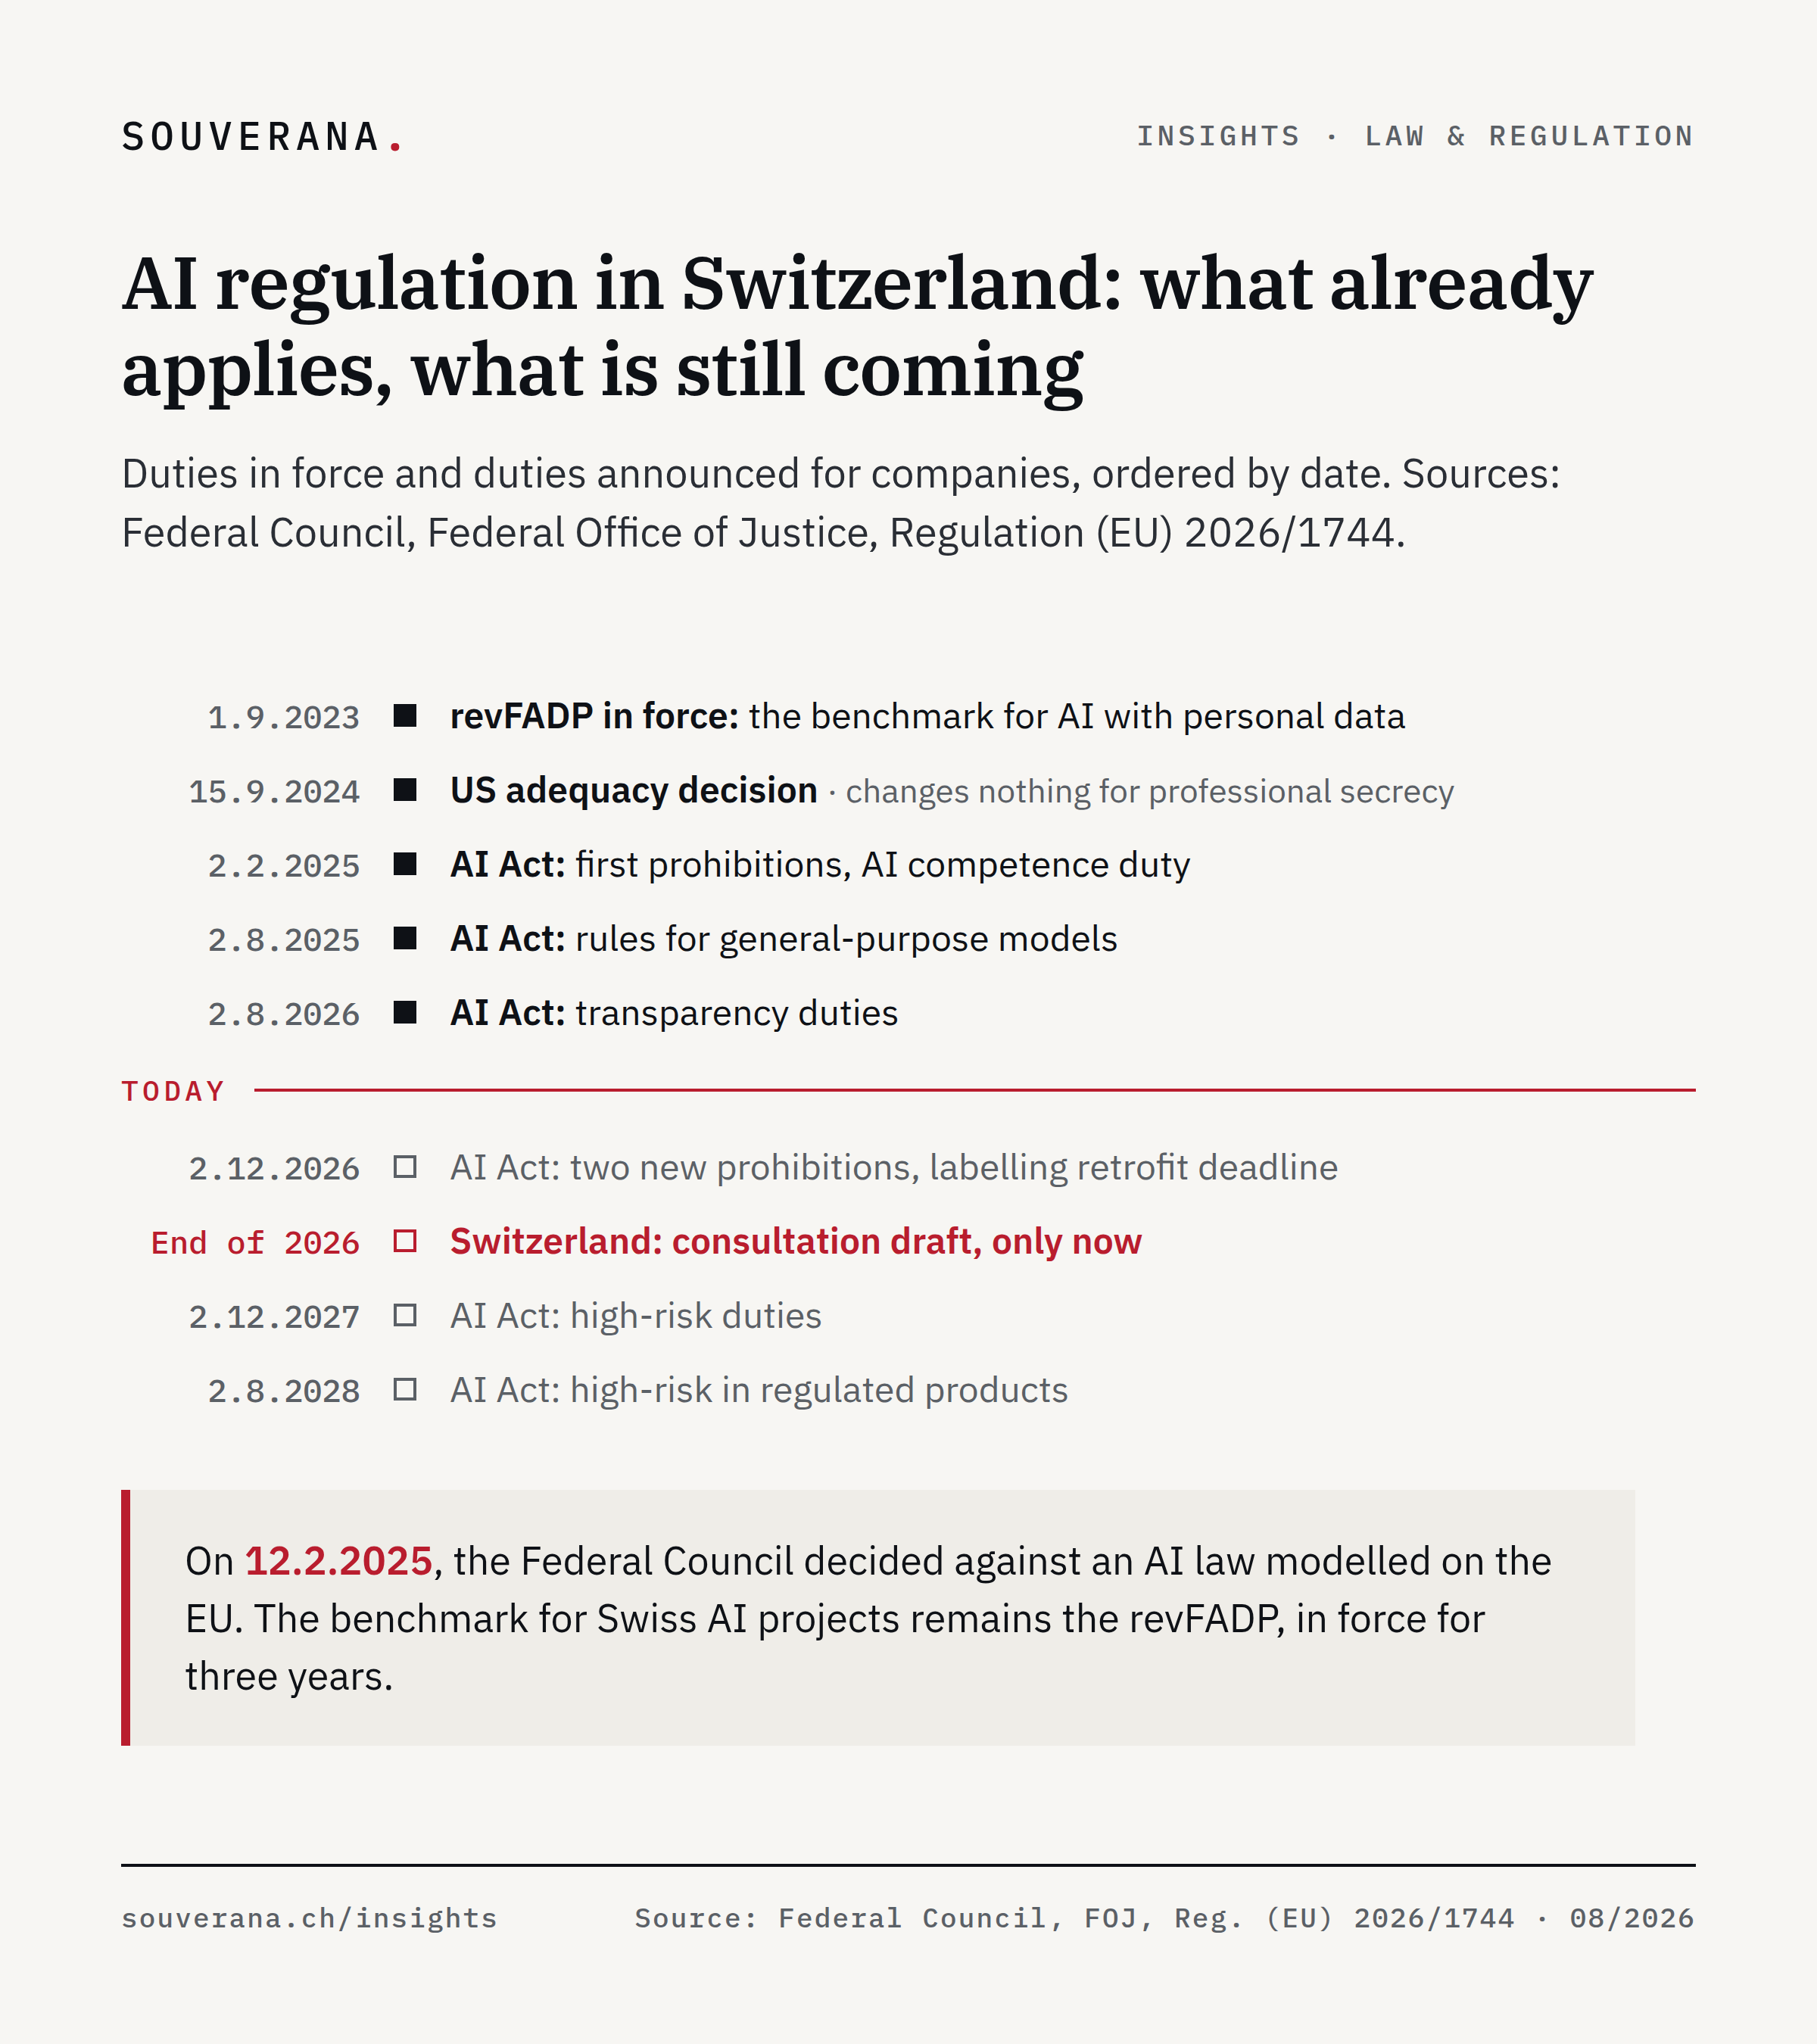
Most conversations about AI regulation revolve around rules that are not yet applicable at all. The data protection law that almost every AI project is actually measured against, by contrast, has applied for nearly three years.
revFADP in force
The revised Federal Act on Data Protection. The rule that AI use in Switzerland is measured against today.
US adequacy decision
Personal data may go to certified US companies without additional safeguards. It changes nothing for professional secrecy.
AI Act: prohibitions and AI competence
Eight prohibited practices, plus the duty to make best efforts to ensure adequate AI competence among employees.
AI Act: rules for general-purpose models
Obligations for their providers, additional ones for models with systemic risk, plus supervisory bodies and sanctions.
AI Act: transparency duties
Chatbots must be recognisable as machines, and AI-generated content must be marked in a machine-readable way. Both duties fall on the provider of the system. For systems placed on the market before this date, the marking duty applies only from 2 December 2026.
AI Act: two new prohibitions
Newly prohibited are AI systems for non-consensual intimate material and for depictions of child sexual abuse.
Switzerland: consultation draft
The first concrete text implementing the AI Convention. The federal government has not said when the consultation procedure will open.
AI Act: high-risk areas
Biometrics, critical infrastructure, education, employment, migration. Pushed back by the AI Omnibus.
AI Act: high-risk in products
AI as a safety component in already-regulated products, such as lifts or toys.
Switzerland: dispatch and Parliament
Evaluation, revised draft, dispatch, then deliberation in Parliament. The federal government names no date for this.
The most recent change is the AI Omnibus, a package that amends the AI Act after the fact: the European Commission proposed it on 19 November 2025, Parliament adopted the negotiated text in June 2026, it was signed on 8 July 2026, and since 27 July 2026 it has been in force as Regulation (EU) 2026/1744. It pushed the high-risk rules back by twelve to sixteen months and simplified a number of things for smaller companies: a simplified form is now available for technical documentation, SMEs may keep quality management leaner, and the training duty explicitly requires no specific level of AI competence.
The AI Act mostly reaches you as a deployer
The AI Act knows two roles, and which one you hold decides almost everything. A provider is whoever develops an AI system and places it on the market or puts it into service under its own name. A deployer is whoever uses such a system under its own responsibility. Because the law has product safety in view, the heavy obligations sit almost entirely with the provider: risk management, documentation, conformity assessment. As a deployer, you essentially ensure transparency and follow the provider’s instructions. Most Swiss companies are, if anything, deployers.
Key figure
5 to 10%Source: Estimate, cited in VISCHER, part 7 of the AI Act series
The role can change, however, and then a light deployer duty becomes a full provider obligation. Whoever applies a general tool to a high-risk task becomes the provider of a high-risk system themselves. The classic example is an HR department that has ChatGPT screen job applications. A chat tool thereby becomes a system that judges people, and the employer takes on the provider role with all the obligations that come with it.
How far the AI Act reaches into Switzerland is shown by comparing a few everyday cases:
| What your company does | Role under the AI Act | What to do |
|---|---|---|
| Employees write text with ChatGPT that also goes to recipients in the EU | Deployer | No special duty. Disclosure only for published text on matters of public interest |
| Chatbot on your own website that also addresses EU customers | Provider and deployer | The bot must be recognisable as a machine, and the duty falls on you as provider |
| ChatGPT screens job applications for positions in the EU | Provider of a high-risk system | Risk management, documentation, conformity assessment, from 2 December 2027 |
| The same candidate screening, but only for positions in Switzerland | No role under the AI Act | The revFADP applies, not the AI Act |
The last row is the most important. The operative text turns on the AI’s output being used in the EU; that the use must be intended appears only in the recital, an explanatory statement preceding the text of the regulation. Where the line to mere accessibility sits is unresolved. A person from the EU applying for a Swiss position is unlikely to be enough on its own.
What Switzerland is planning
The federal government had three paths to choose from: continue as before, adopt the Council of Europe’s AI Convention, or additionally mirror the EU AI Act. On 12 February 2025, the Federal Council chose the middle path. Where legislative changes become necessary, they should be as sector-specific as possible; a general, cross-sector regulation is to be limited to areas central to fundamental rights, such as data protection.
For the private sector, this means little immediate change. Swiss laws mostly set out general principles and therefore also fit technologies that did not yet exist when they were written. Many of the Convention’s requirements are therefore already met.
One detail shows how early-stage all of this still is: Switzerland signed the Convention on 27 March 2025, but has not ratified it. It is not even in force yet, since that requires five ratifications, including three Council of Europe member states. So far, only the EU has ratified it.
From the federal government’s legal analysis, four adjustments can be anticipated that could affect companies:
- Partially automated decisions. Today the revFADP applies only where a machine decides alone. In future, the case where an AI prepares a decision and a human merely confirms it will likely also be covered. There are many such cases. In the EU, the Court of Justice has already brought this case within Art. 22 GDPR, provided the human decision depends decisively on the automated value (SCHUFA, C-634/21). Whether Switzerland will draw the line more narrowly or more broadly remains open.
- A register of AI applications. For state bodies, this is fairly certain to come; for private companies, at most in isolated areas.
- Labelling of AI content. Swiss law so far has no general labelling duty. Here the federal government sees a genuine gap.
- Impact assessment. A duty to assess in advance the effects of an AI project on the people affected, related to the data protection impact assessment under the revFADP.
Whether a new AI authority will be created has not yet been decided. In the minimal variant, oversight would stay with today’s bodies: the financial market supervisor FINMA, the data protection commissioner FDPIC, and the communications commission ComCom. These three would gain investigative powers, but not sanctioning powers. The more far-reaching variant explicitly leaves open additional sanctioning powers and a new coordination body. FINMA is already working on its supervisory practice today, based on current law.
The hard line remains professional secrecy
Since September 2024, personal data may go to US companies certified under the Swiss-U.S. Data Privacy Framework without additional safeguards. The decision says nothing about the US CLOUD Act. Part of legal scholarship reads this silence as an answer: that the Federal Council has tacitly rejected the view that the CLOUD Act is incompatible with the Swiss legal order. Cantonal data protection authorities continue to see it differently. For ordinary data protection purposes, the question hardly matters in practice any more; legally, it is not conclusively resolved.
This relief does not apply to professional and official secrecy. Whoever falls under Art. 320 or 321 of the Swiss Criminal Code, meaning authorities, law firms, medical practices and hospitals, must assess, before moving to a foreign cloud, whether foreign authority access is to be expected. The same applies to banks via banking secrecy in the Banking Act. No law prescribes a procedure for this; in practice, the Foreign Lawful Access Risk Assessment, or FLARA, has become the standard. The contract also needs clauses that standard offerings rarely include: a confidentiality duty that binds the provider itself; plaintext access limited to people who need it for their work; and a commitment to resist disclosure orders.
For most companies, sovereignty is a business decision about dependency, cost and credibility. For secrecy holders, it is a legal requirement. We break down how much sovereignty is needed in which case in What is sovereign AI.
How to get started
A company that takes the following four steps already meets a good part of what future Swiss regulation is likely to require.
- 01
Inventory
List where AI is used in your operations, including bought-in software that already contains AI functions.
- 02
Check contracts
Check four points per tool: data processing agreement, confidentiality, no training on your data, free use of the outputs.
- 03
A one-page policy
Which tool is approved for which data class, and who in the company is responsible for it.
- 04
A ripcord
A short list of questions. If one of them applies, employees ask the responsible person and do not decide on their own. This is how the sensitive cases are caught.
In practice, we more often see a blanket ban. Companies prohibit AI because nobody wants to take responsibility for approving it. The ban then pushes usage onto private accounts, where the company has neither contract nor control. Shadow AI arises exactly there.
The further parts of the series explore the areas of this map in depth: the revFADP, professional secrecy, AI governance and the EU AI Act.
Frequently asked questions
- Is there an AI law in Switzerland?
- No. On 12 February 2025, the Federal Council decided against a dedicated AI law modelled on the EU AI Act. Instead, it intends to ratify the Council of Europe's AI Convention and adapt existing law sector by sector where needed. A consultation draft is due by the end of 2026; the date of the dispatch to Parliament is open.
- Does the EU AI Act apply to Swiss companies?
- Only in narrowly defined cases. The EU AI Act, the EU's AI law, applies to Swiss companies that place an AI system on the EU market or whose AI output is used in the EU. A company that uses AI exclusively for Swiss purposes is, as a rule, not covered. Exactly where the line to mere accessibility in the EU sits remains unresolved.
- What does the revFADP require when using AI?
- The revised Federal Act on Data Protection (revFADP) requires what any data processing requires: the processing principles, a data processing agreement with the provider, adequate security, transparency and, for high risk, a data protection impact assessment. Unlike in the EU, a private company needs no statutory basis for this. Fines of up to CHF 250,000 target natural persons and require intent.
- When does a company become a provider under the AI Act?
- Whoever develops an AI system and places it on the EU market under their own name is a provider. The role can also arise unintentionally: whoever uses a general tool such as ChatGPT for a high-risk task that the AI Act regulates strictly, for instance to screen job applications, thereby becomes the provider of a high-risk system themselves.
- May holders of professional secrecy use AI in the cloud?
- Yes, but with an additional check. Since September 2024, the Federal Council's adequacy decision has eased the transfer of personal data to certified US companies. Professional and official secrecy, the statutory duty of confidentiality, is unaffected by it. Before moving to a foreign cloud, assessing the risk of foreign authority access is the standard step.
Share this article
Ready-formatted graphics and a suggested post for your LinkedIn feed: download, copy, post.
Suggested post
Are you holding off on AI projects until Switzerland has its own AI law?

Then you will be waiting a long time. On 12 February 2025, the Federal Council decided against EU-style regulation. The first draft for consultation is not due until the end of 2026, and when a dispatch will reach Parliament remains open.

The real benchmark has existed for years. The revised Federal Act on Data Protection (revFADP) has applied since 1 September 2023 and measures every AI project involving personal data. Add copyright law, your own client contracts, and professional secrecy for eighteen professions. The EU AI Act, the EU's AI law, only applies where there is an EU nexus, and its heavy high-risk duties do not begin until 2 December 2027.

Our conclusion: there is nothing to wait for. A company that inventories its AI applications today, checks its provider contracts and issues a policy for employees already meets a good part of what future Swiss regulation is likely to require.

The article covers the full timeline, a table of everyday cases by provider and deployer role, and a worksheet with the questions that trigger a closer look. Link in the comments.

#AI #Switzerland #revFADP #Compliance